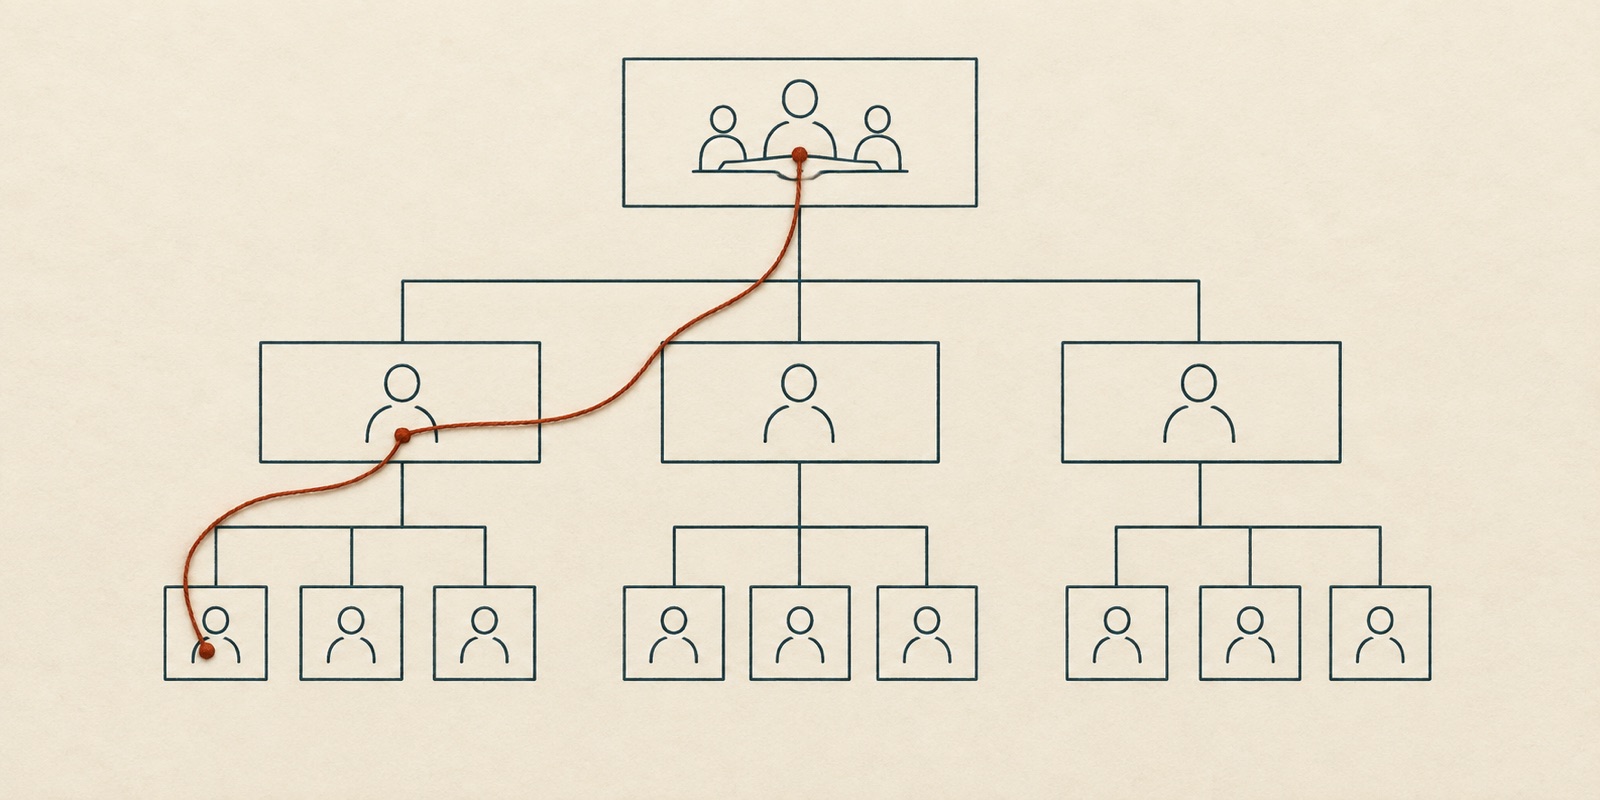
In October 2023, the FDIC and the Texas Department of Banking issued a consent order that overhauled a Texas bank’s access-review process.
The bank agreed to complete a full review of user access within 30 days. It also agreed to have access to its systems reviewed and ratified at least quarterly, with each ratification recorded in its board minutes, plus a quarterly access review by someone other than the person who did the work, reported to the board.
By putting access in the board minutes, the fix worked. The FDIC eventually terminated the 2023 order in 2025, but the event illustrates a landscape shift for financial institutions: even though IT grants the access, the board is accountable for it.
Why start with access? Because access is the foundational layer of security. Fraud controls, monitoring, incident response and vendor oversight all assume you know who can reach what at any given time. If you can control who has access, everything else is downstream. Get it wrong, and every other control is working from a bad list.
The Three Lines
Most bank and credit union leaders know the “three lines” model. In its current form, the lines describe three distinct roles:
- Management runs the operation and owns its risks. In the model’s terms it holds both first-line roles, meaning the people who deliver the service and own the controls (including who gets access to what, and taking it away), and second-line roles, meaning the risk and compliance specialists who set expectations, monitor and challenge.
- Internal audit is the third line, and is independent of management. It gives the board objective assurance that it all works.
- The governing body, meaning your board, is accountable for oversight. It delegates responsibility to management and provides the resources to do the job.
It’s worth noting that examiners aren’t one of those lines. They’re outside the institution, and they check in periodically. Nothing in the model makes the exam part of your controls.
The Risk Remains the Same, Regardless of Examination Schedule
There were two changes made this year that mean the outside check will catch less:
- Banks: starting November 2, a new OCC and FDIC rule limits formal “matters requiring attention” to problems that could reasonably be expected to cause material financial harm, or that break a banking law or regulation. Lesser issues become informal observations you aren’t required to act on. The rule doesn’t cover credit unions or Fed-supervised banks.
- Credit unions: NCUA says some well-run credit unions could now go up to 24 months between exams.
However, less oversight doesn’t mean less risk. An access review is how you find the teller who can still move money, the former employee who can still log in, and the vendor account nobody owns. Those are the problems that can turn into real losses. It’s now more likely that you’ll be the one who finds them, or that an incident will.
Where it Goes Wrong
When access governance fails badly, the record often points higher than IT.
At Copper & Glass Federal Credit Union, according to NCUA’s Inspector General, an exam as of December 31, 2022 found a teller transacting on her own and relatives’ accounts. The board promoted her to manager in 2024. As manager she had sole access to the card servicing system, and she used it to raise credit lines on her own and her spouse’s accounts. The credit union failed after writing off about $3.5 million. NCUA’s Inspector General wrote that the board “lacked the knowledge and capabilities to oversee the credit union effectively.”
At the Texas bank, the regulators put access reviews on the board’s agenda and in its minutes.
In both cases, the board ended up being at the center of the discussion.
Five Questions Your Board Should Be Able to Answer
A board doesn’t need to review access itself. Instead, it needs management to be able to answer these, with evidence, at any meeting:
- Who has access to our critical systems? That means the core, wire and ACH, the card platform, and online banking administration, and the network.
- When were those reviews last done, and by whom? Reviewed by the managers who understand the access, with the results on record.
- What did the reviews remove? A review that never removes anything is a signature, not a control.
- What are the various permissions, and are duties properly separated? In addition to knowing who has access, there needs to be clarity into exactly what permissions each individual has and whether they’re appropriate (e.g. the person approving wires shouldn’t be able to send wires).
- How fast does access go away when someone leaves, changes roles, or a vendor contract ends? Measured, not assumed.
If those answers take a month of spreadsheets, screenshots, and help desk tickets to assemble, the board is getting reassurance, not evidence.
Fix It, or Risk Having It Fixed For You
When access governance fails at the top, someone else writes the fix. The Texas bank’s 2021 order restructured its board so that most of its directors came from outside the bank. Its 2023 order put access reviews into the board minutes, every quarter. Copper & Glass never got a fix. The credit union was liquidated, and NCUA’s Inspector General wrote that its board “lacked the knowledge and capabilities to oversee the credit union effectively.”
Nobody wants to have that conversation. The cheaper one happens now, while 2027 budgets are still open.
If you sit on the board: at your next meeting, ask management to answer the five questions above, with evidence. If the answers take a month of spreadsheets to pull together, fund the fix.
If you run IT or compliance: don’t wait to be asked. Take the five questions to your board this quarter, show them what it takes to answer, and put the cost of doing it properly in the 2027 budget. Your auditors will ask anyway. It’s better for the board to hear it from you first.
IT grants the access. The board is accountable for it. Make sure your board has seen the evidence before someone else asks for it.
Interested in Provision IAM? Talk to us.
Sources
- FDIC Consent Order, Herring Bank, FDIC-23-0036b (Oct. 2023). orders.fdic.gov
- Texas Department of Banking / FDIC, Herring Bank Order 2021-015 (FDIC-21-0066b), Oct. 2021. dob.texas.gov
- FDIC, FDIC Issues Enforcement Orders for April 2025 (May 30, 2025), listing termination of FDIC-23-0036b. content.govdelivery.com
- The Institute of Internal Auditors, The IIA’s Three Lines Model (2020; updated Sept. 2024). theiia.org
- OCC/FDIC final rule, Unsafe or Unsound Practices; Matters Requiring Attention, 91 FR 56004 (effective Nov. 2, 2026). fdic.gov
- NCUA, 2025 Annual Report (p. 2). ncua.gov
- NCUA, No Regulation-by-Enforcement Policy Statement. ncua.gov
- NCUA Office of Inspector General, OIG-26-10, Copper & Glass FCU (Sept. 24, 2026). ncua.gov